An enterprise AI layer IT can govern.
Five microservice layers, deployment on Azure or customer infrastructure, no copies of source data and no writes without authorisation.
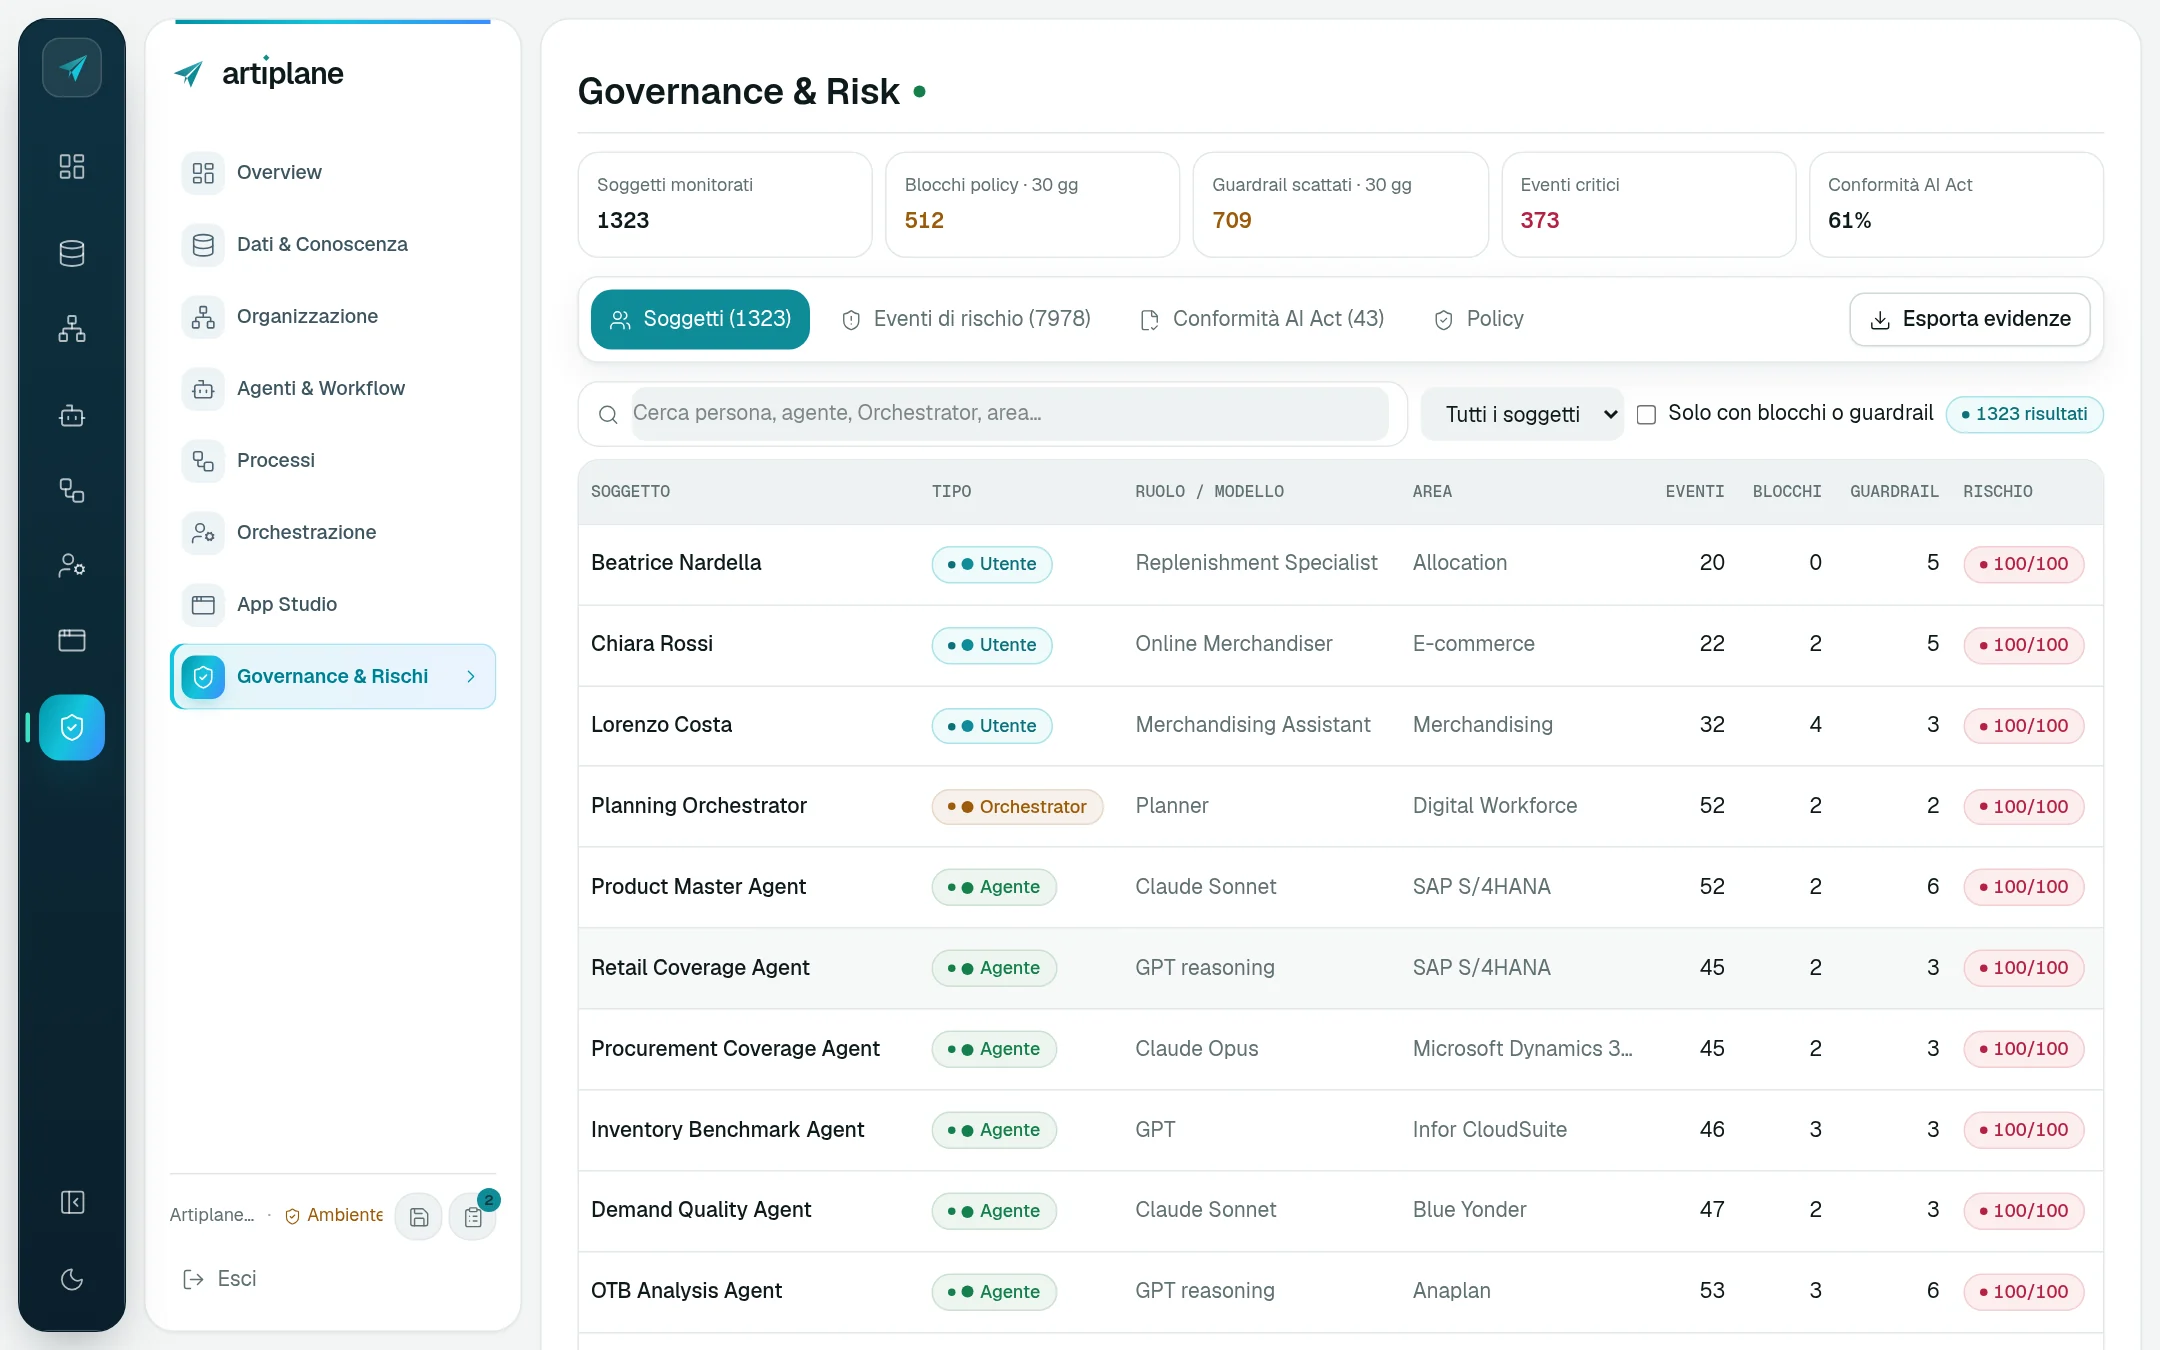
- 1.323monitored subjects
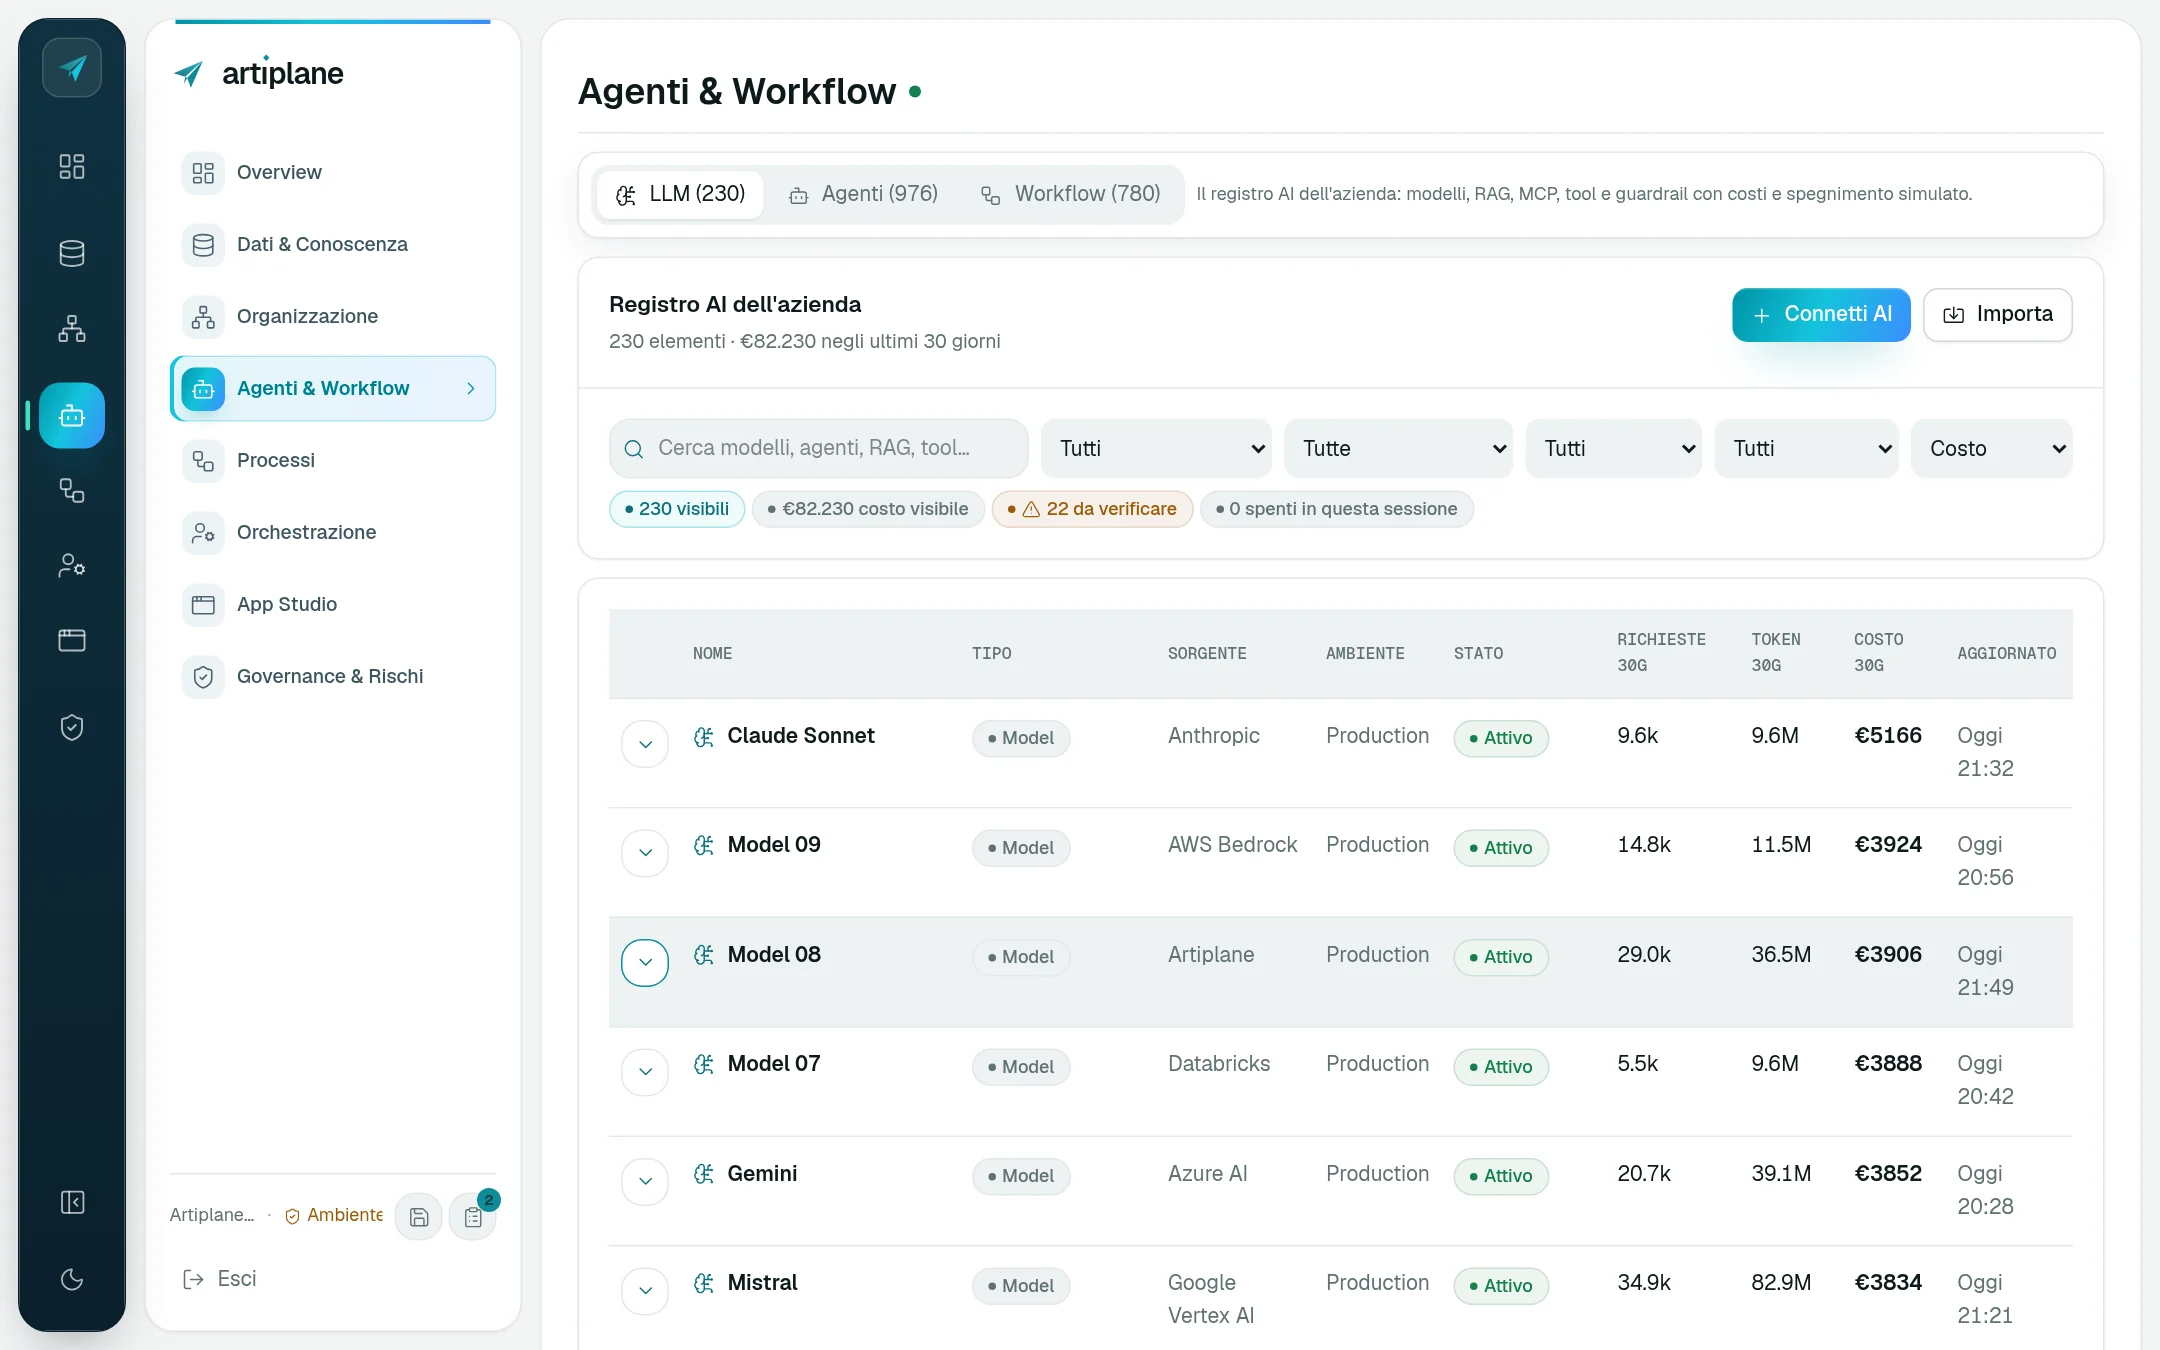
- 230registered AI elements
- 5layers, one model
For IT and Chief AI Officers
Eight answers before the security review.
Architecture
Architecture
Five microservice layers with explicit contracts: Knowledge, Semantic, Organization, Orchestration, Experience. Versioned APIs and events between layers; only the first touches systems.
Deployment
Deployment
Managed Azure in an EU region, customer cloud (Azure, AWS, Google Cloud) or on-premise Kubernetes. Network, keys and identity remain under customer control.
Integration
Integration
Connectors via API, OData, CDC, files and events; first access read-only with least-privilege credentials. Versioned mapping to the canonical model.
Data
Data
No parallel data lake: systems remain the source of truth. Every value keeps source lineage, freshness and permissions; retention is configurable.
Identity and access
Identity and access
Enterprise SSO, roles, object and action permissions, market and brand scopes. The server revalidates every sensitive request.
LLM gateway
LLM gateway
Azure OpenAI, OpenAI, Anthropic Claude, AWS Bedrock and open-weight models chosen per task. Customer LLM contracts integrated, with budgets and costs by area.
Governed writes
Governed writes
Agents propose, they do not execute: every write is a registered action with contract, approval threshold, idempotency and execution record.
Lifecycle and audit
Lifecycle and audit
Draft → Test → Production with Change Requests, versions and rollback. SHA-256 hashed logs, configuration audit and EU AI Act controls.
Control Plane
Architecture, connectors and governance.
Deployment
Runs inside the customer perimeter
Azure reference, deployable on AWS, Google Cloud, private cloud or on-premise. Data stays where it is; models are chosen by contract and policy.
- Microsoft Azure
- AWS
- Google Cloud
- Private cloud
- On-premise
Customer perimeter · tenant, VNet/VPC, identity provider
- Super Apps
- Admin console
- Chat
- API
- 1Knowledge
- 2Semantics
- 3Organisation
- 4Orchestration
- 5Experience
- SAP S/4HANA
- Salesforce
- Microsoft 365
- PLM
- WMS
- POS
- Data lake
- Anthropic Claude
- OpenAI
- Azure OpenAI
- AWS Bedrock
- Google Gemini
- Private models
- n8n
Product reference architecture. Topology, sizing and controls are confirmed with the customer’s IT during technical review.
Operational control
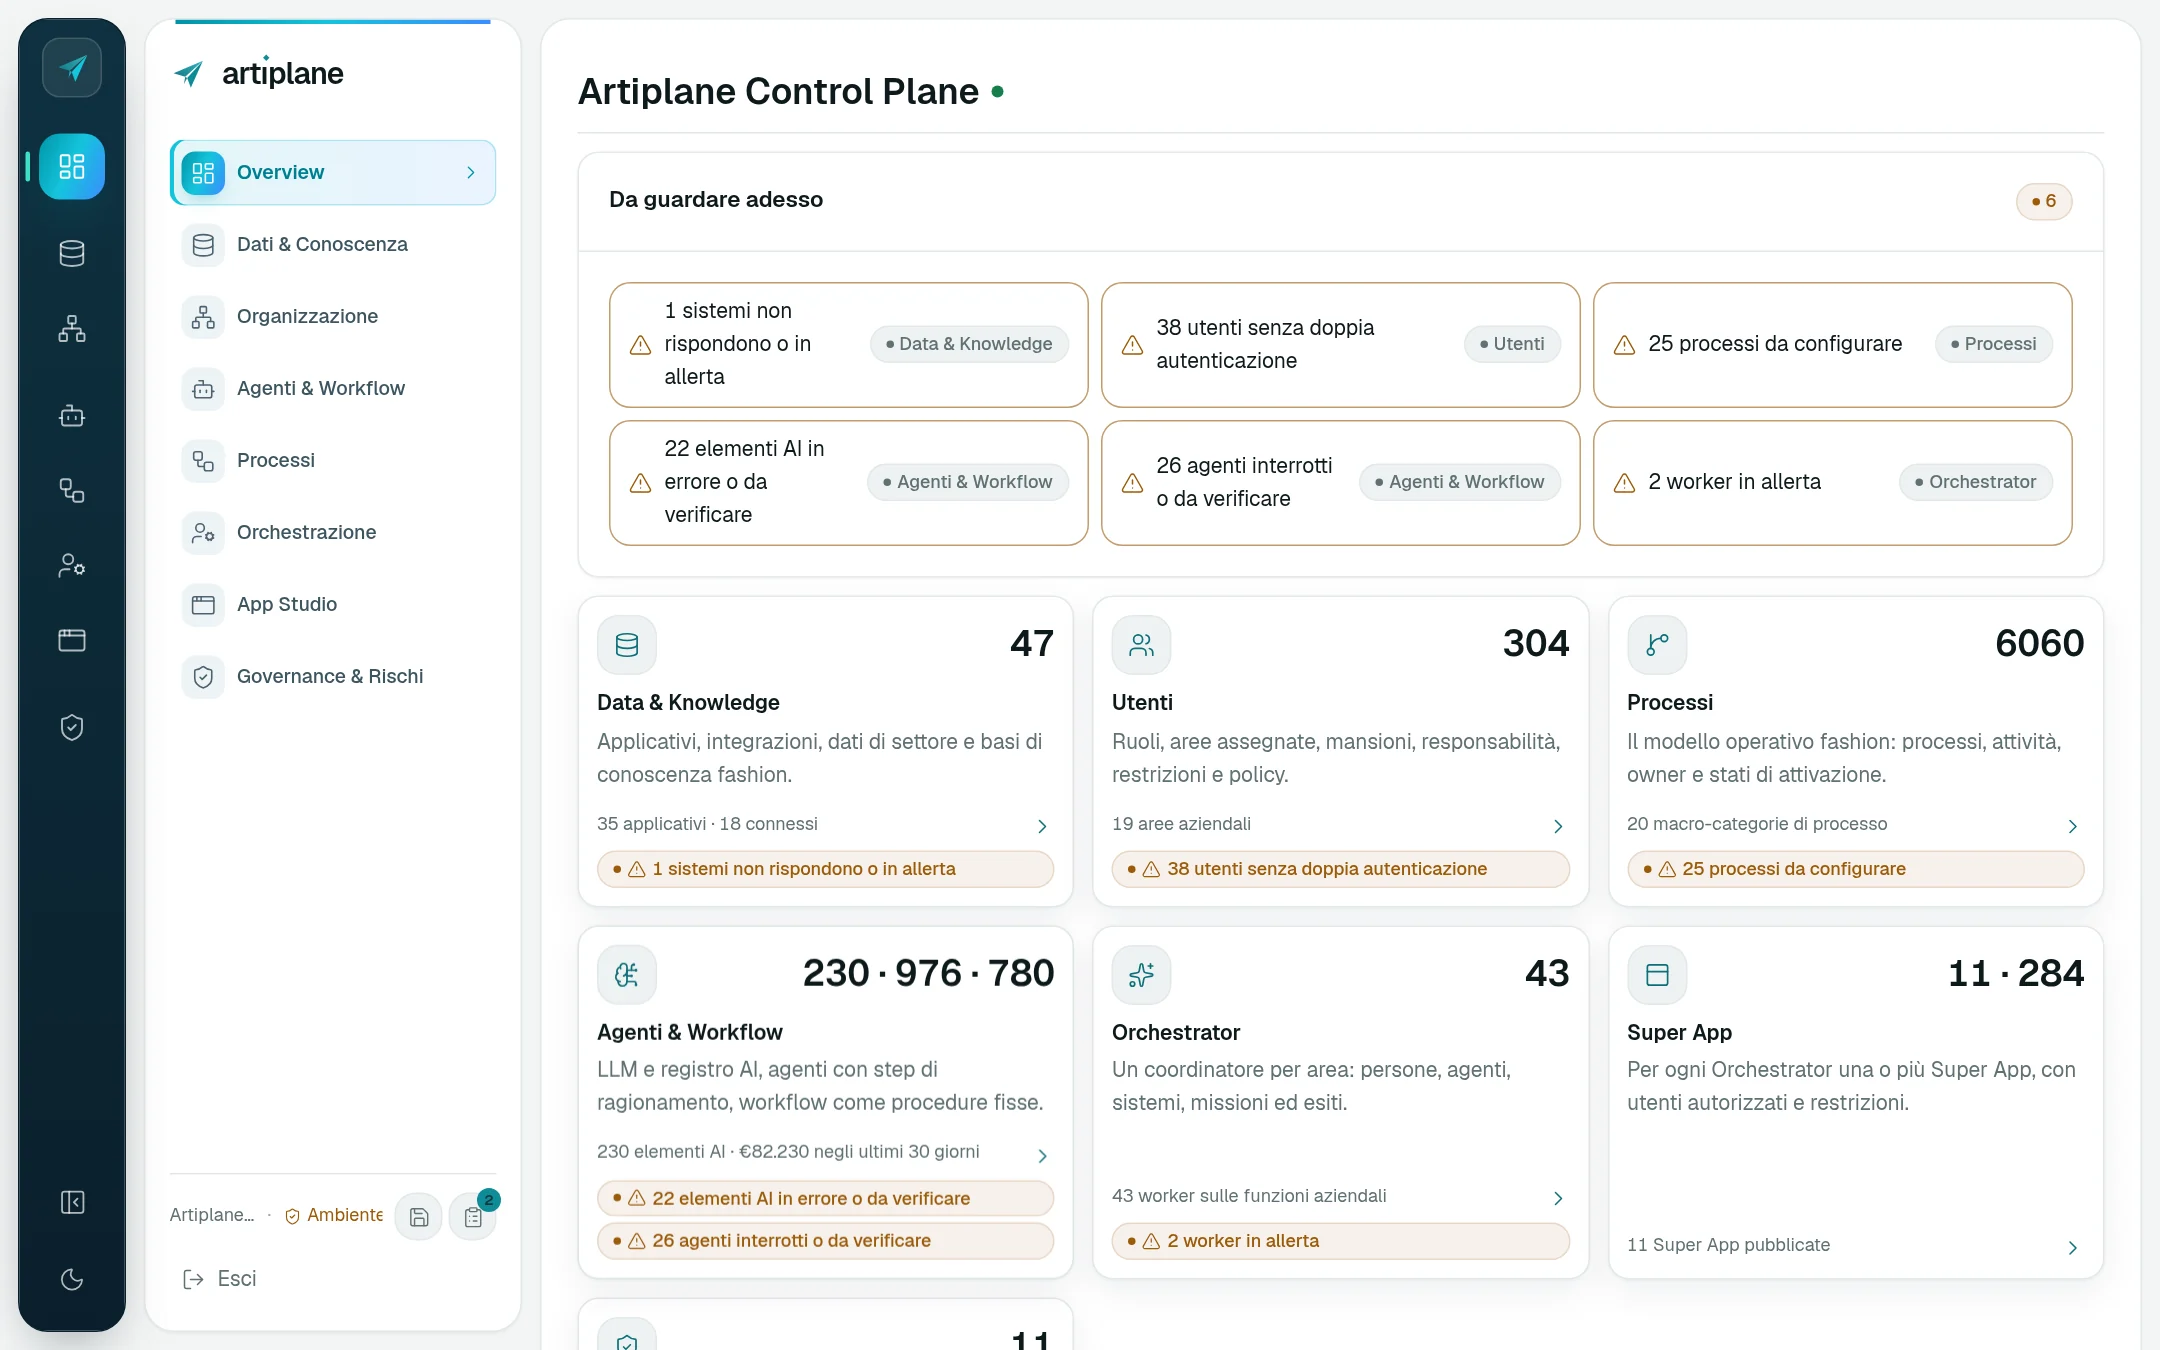
What IT sees every day
Console, AI registry, governance, audit and identity.
Real product screens · Atelier Nova Group reference tenant
Controls
Security control matrix
Product specification: each control is validated on the customer tenant.
Assess Artiplane on your landscape.
Systems, identity, AI models and deployment constraints: we define scope and reference architecture together.